

// AI
AI governance and AI security: an approved path instead of bans
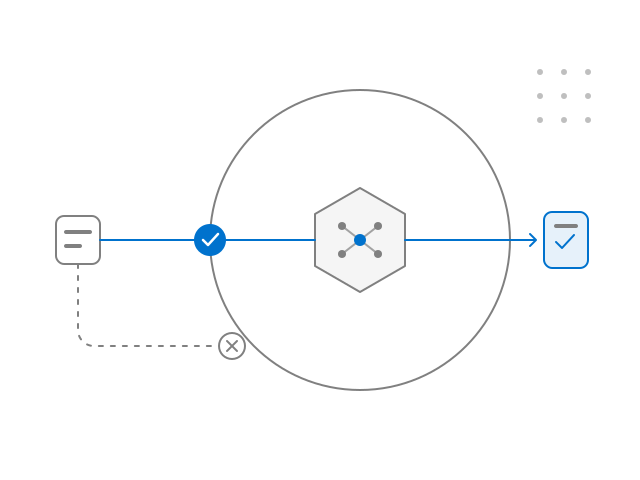
A ban is not a control. People go back to personal accounts because the approved path is slower than the workaround. We set up AI rules that work in your systems: in access, logs, data filters and tests.
// In short
What is AI governance?
AI governance defines who may use AI, with which tools and on which data, and enforces it in your systems: in SSO sign-in, permissions, data filters and logs. AI security means testing chatbots, agents and AI-written code. For companies rolling out Copilot or ChatGPT Enterprise that have to show compliance with the AI Act.
We start with strategy: where AI adds real value for your business, which risks you accept and which path to approve first, so that nobody needs a personal account anymore.
// What we do
From inventory to agent testing
01Inventory
Inventory of AI tools and use cases
Who uses what, on which data and from which account. With a risk classification and the vendor's role.
02Policy in the system
An AI policy your systems enforce
SSO sign-in, access that mirrors existing permissions, prompt logging and DLP rules for Copilot and ChatGPT Enterprise.
03AI Act
AI Act obligations
Transparency under Article 50, a check of whether a system falls under Annex III, and support for AI literacy in your team.
AI Act and ISO/IEC 4200104LLM testing
Testing chatbots, RAG and agents
Following the OWASP Top 10 for LLM Applications 2026 and the OWASP Top 10 for Agentic Applications: prompt injection, data leakage through RAG, excessive agent permissions.
05AI-written code
Review of AI-written code
Secrets in code, dependencies suggested by the model, missing validation and access control. With fixes your team understands.
06Local model
Private or on-premises model
Whether a chosen use case can run on a model in your own infrastructure, and what that costs. One example: FutureCode Evidence Box runs its AI models inside your network, with no internet access.
// AI Act deadlines
What applies now and what comes later
The transparency obligations of Article 50 apply from 2 August 2026. Obligations by role, prohibited practices and an AI management system under ISO/IEC 42001 are covered on our AI Act and ISO/IEC 42001 page.
Art. 50
End of the grace period for marking generated content
Applies to generative systems placed on the market before 2 August 2026 (Article 50(2)).
Annex III
High-risk systems listed in Annex III
For example, AI used in recruitment and credit scoring.
All AI Act deadlines
As of . Source: Regulation (EU) 2026/1744.
First step: one approved AI path in 6 weeks
AI strategy first
Use cases with real value, an acceptable level of risk and the order of rollout.
Inventory of tools and use cases
What is used today, officially and from personal accounts, and on which data.
Risk classification and vendor assessment
Your role under the AI Act, the terms of your vendor contracts and where the data goes.
A private option for one use case
Whether that use case can run on a model in your own infrastructure.
The result: an approved path with access control and logging in one department
Fixed scope and date, agreed in writing before we start. Request the first step
// Scope
What we do, and what we don't
We do
- An AI strategy with a list of use cases and a risk threshold
- An AI inventory and risk classification
- An AI policy built into SSO, permissions, logs and DLP
- Testing of chatbots, RAG and agents, and review of AI-written code
- Assessment of a private or on-premises model
We don't
- Bans that nobody enforces
- An AI policy copied from a template with no change in your systems
- An AI Act compliance certificate, because no such document exists
- Reselling licenses for models and tools
The AI Act does not, as such, require an AI policy or an AI register. Both are still the simplest evidence that you are in control of how your company uses AI.
// Read more
Related topics and services
// FAQ
Questions about AI governance
Does the AI Act require an AI policy?
Not as such. The AI Act requires neither an AI policy nor an AI register. It does require, among other things, transparency under Article 50 and support for AI literacy among staff (Article 4). A policy and a register are the simplest evidence that you meet those obligations (as of 24 September 2026). Obligations by role are on our AI Act and ISO/IEC 42001 page.
What about Copilot?
Microsoft 365 Copilot sees what the user sees. If permissions in SharePoint and Teams are too broad, Copilot will surface that quickly. We start by reviewing permissions and sensitivity labels, then set up logging and DLP rules.
How do you test a chatbot?
By hand, following the OWASP Top 10 for LLM Applications 2026. We try to inject prompts, pull data out of the RAG store, bypass restrictions and trigger actions the agent should not have permission for. Every finding comes with evidence and a recommendation, and we retest the fixes. Source: OWASP.
Can we run a model locally?
For many use cases, yes: document search, summaries and classification, for example. We test answer quality, hardware and running costs on one use case before you decide on a larger rollout. Your data then stays inside your network.
Who in the company should own this?
One person with a mandate from the board, usually from IT, security or compliance, plus use case owners in the business units. We help set up these roles and a simple approval process for new tools.
Let's start with one approved path
Tell us which department already uses AI, officially or not. We reply within one business day, with questions about tools and data.
Request the first stepPrefer to talk first?
30 minutes about how your company uses AI, with no sales pitch.
Book a 30-minute call (opens in a new tab)