

// Security
Penetration testing of applications and systems, with a retest of fixes
Your fix order is set by a scanner, not by business impact. And the system everyone describes as "it works, just don't ask how" is usually the one serving customers. We check real attack paths by hand and retest your fixes at no extra cost.
// In short
What is a pentest?
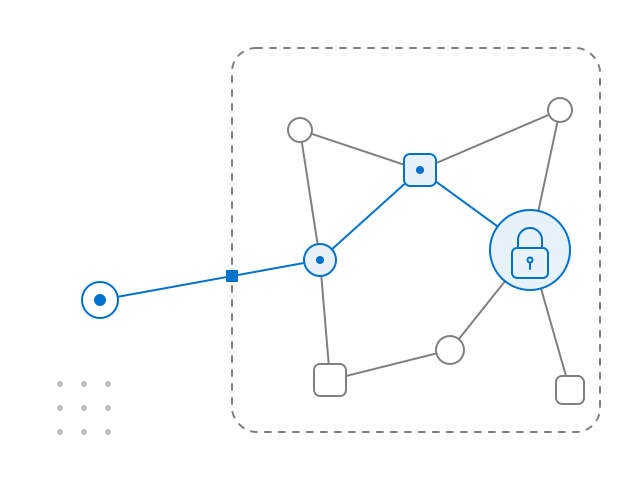
A penetration test is a controlled attempt to break into an application, API, cloud or network, done by a human tester and not by a scanner alone. It shows which vulnerabilities can really be exploited and what that means for the business. For teams that want to know what to fix first before a release, an audit or a customer security questionnaire.
// What we test
From applications to AI features
We test the routes to your data and customers, not just what is easy to scan.
01Applications
Web applications and APIs
Authentication, authorization, business logic, sessions and input handling, following OWASP WSTG and ASVS. For a full requirement-by-requirement check, see our OWASP ASVS assessment.
02Cloud
Cloud configuration
Identities and roles, networking, storage, secrets and logging in Azure or AWS.
03Network
Internal network
Segmentation, services and privileged accounts, tested with non-destructive techniques.
04Integrations
Integrations and permissions
API keys, service accounts and cross-system permissions that nobody usually reviews.
05AI
AI and LLM features
Prompt injection, data leakage through RAG and excessive agent permissions, following the OWASP Top 10 for LLM Applications 2026.
AI security06AI-written code
Code written with AI assistants
Secrets in code, dependencies suggested by the model, missing validation and access control.
// How we test
From scope to retest
Scope and rules of engagement
Agreed in writing: systems, test accounts, time windows and the test type (black, gray or white box).
Manual testing
We check real attack paths following OWASP WSTG, ASVS and PTES. A scanner is where we start, not the result.
Report with evidence
Every finding has evidence, reproduction steps and a priority based on business impact, not only a CVSS score.
Retest of fixes
We retest your fixes as part of the engagement and add the result to the report.
First step: one system and its integrations in 4 weeks
Attack surface map
Entry points, dependencies and the integrations that feed the system.
Review of permissions and integrations
Service accounts, keys and roles that grant more than they should.
Backlog with owners and dates
Findings assigned to people, prioritized by what would really stop the business.
The result: at least one critical path closed and confirmed by a retest
Fixed scope and date, agreed in writing before we start. Request the first step
// How we price
How we price a penetration test
The price depends on the number of tester days. You get it in writing before we start, together with the scope, and we don't change it mid-test without your consent.
What drives the number of days
- Number of user roles and permission levels
- Number of API endpoints and functions to check
- Number of environments and integrations
- Test type: black, gray or white box
Always included
- Scope and rules of engagement agreed in writing
- Manual testing, not just a scanner
- A report with evidence and a priority for every finding
- A walkthrough of the results with your team
- Retest of fixes at no extra cost
We don't quote without a scope. After a short call you get a written estimate of days and a proposed date.
// Scope
What we do, and what we don't
We do
- Manual testing of web applications, APIs and internal networks
- Review of Azure and AWS cloud configuration
- Testing of AI and LLM features and review of AI-written code
- A report with evidence and business priorities
We don't
- Scanner output relabeled as a pentest
- Destructive tests in production
- A TLPT or TIBER label on a test that does not meet their requirements
- Formal KSC audits (NIS2 in Poland): we don't perform them
// Read more
Related topics and services
More on application and access security on our blog:
// FAQ
Questions about penetration testing
Penetration test or vulnerability scan?
A scan automatically finds known vulnerabilities and produces a long list. A penetration test checks by hand which of them can be chained into a real attack and what it would give an attacker. Run scans regularly, and a pentest before an important release or after a major change.
How long does a test take and what drives the cost?
The first step, one system with its integrations, takes 4 weeks. The price is the number of tester days and depends on the number of roles, API endpoints, environments and the test type. You get the estimate in writing before we start.
Do you test in production?
Only with non-destructive techniques, after the rules of engagement are signed and within an agreed time window. Where possible, we test in a staging environment configured like production.
What is in the report?
A management summary, findings with evidence and reproduction steps, a risk rating with a business priority, fix recommendations and the retest result. The report works as evidence for an auditor and as an attachment to a customer security questionnaire.
Does a pentest help with NIS2 and DORA?
Yes, as evidence: it shows what was tested, what was found, what was fixed and when the fix was confirmed. For entities in Poland it does not replace a formal KSC audit (Article 15), and it is not a TLPT under DORA.
Let's start with one system
Point us to a system that serves customers or accepts data from outside. We reply within one business day, with questions about scope and timing.
Request the first stepPrefer to talk first?
30 minutes about the test scope and what drives the number of days.
Book a 30-minute call (opens in a new tab)