

AI Act · ISO/IEC 42001
AI Act compliance: obligations by role and ISO/IEC 42001
The AI Act's transparency rules have applied since 2 August 2026, and the obligations for high-risk systems in Annex III follow on 2 December 2027. For each AI system we establish your role and what follows from it, then build one management system with owners and evidence around it.
// In short
Your AI Act obligations depend on your role
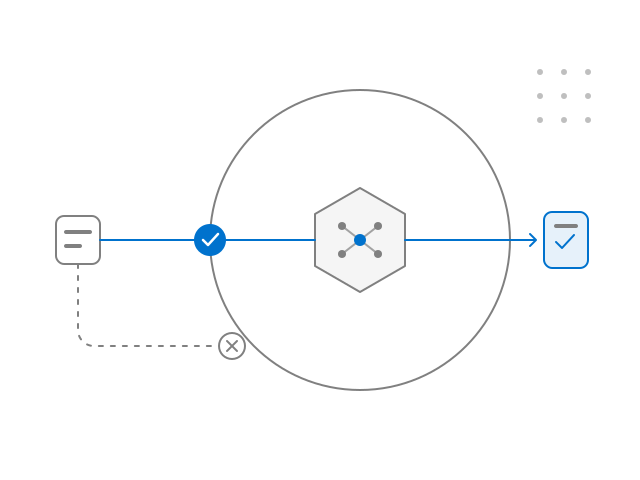
The AI Act, Regulation (EU) 2024/1689, splits obligations by role: a provider of an AI system has different duties from a deployer. Some already apply: prohibited practices since 2 February 2025, Article 50 transparency since 2 August 2026. ISO/IEC 42001:2023 is the AI management system standard that turns these duties into one process with owners and evidence.
// What we do
From an AI system register to a management system
We start with the role and risk class of each system. Only then is it clear which of the obligations below apply to you.
01Role
AI system register with your role
A provider develops an AI system, or has it developed, and places it on the market or puts it into service under its own name. A deployer uses an AI system under its authority. One company is often both.
- Systems and models, including those inside SaaS tools
- Your role for each system and a business owner
- Risk class with the reasoning written down
02Article 50
Transparency that already applies
Providers tell people they are interacting with an AI system and mark synthetic output in a machine-readable format. Deployers disclose deep fakes and AI-generated text published to inform the public on matters of public interest, and tell people when emotion recognition or biometric categorization is used on them.
- Notices on chatbots and voice assistants
- Marking of generated images, audio, video and text
- Publishing rules for AI-assisted content
03Prohibitions
Review of prohibited practices
The Article 5 prohibitions have applied since 2 February 2025. Two more follow on 2 December 2026: non-consensual intimate deep fakes and child sexual abuse material.
- Use cases compared with the list of prohibitions
- Safeguards in generative systems
- A dated decision with its reasoning
04High risk
High-risk systems and deployer duties
Systems listed in Annex III, such as AI used in recruitment or credit scoring, carry obligations from 2 December 2027. Deployers use them according to the instructions for use and assign human oversight to people with the necessary competence and authority (Article 26).
- Classification of each system with its reasoning
- Human oversight with a named person responsible
- Provider instructions turned into procedures
05Article 4
AI literacy
As amended by Regulation (EU) 2026/1744, providers and deployers take measures to support the development of AI literacy among staff and other people who operate AI systems on their behalf.
- A plan matched to roles and the systems in use
- Records of who completed which module and when
- Updates when a new tool arrives
06ISO/IEC 42001
AI management system ready for certification
Scope, policy, risk assessment of AI systems, roles, internal audit and management review. If you already run an ISMS under ISO/IEC 27001, we connect the two instead of building a second one next to it.
- Scope of the AI management system
- Gap analysis against ISO/IEC 42001
- Evidence from systems, not just procedures
// Deadlines
AI Act dates still ahead
Articles 5 and 50
Two new prohibitions, end of the marking grace period
The Article 50(2) grace period covers generative systems placed on the market before 2 August 2026.
Annex III
High-risk systems listed in Annex III
For example, AI used in recruitment and credit scoring.
Annex I
AI in products covered by sectoral legislation
High-risk systems under Annex I, for example in machinery and medical devices.
Regulation (EU) 2026/1744 (opens in a new tab)
As of . Sources: Regulation (EU) 2024/1689 (AI Act), Regulation (EU) 2026/1744. In Poland, the national act on AI systems (Dz.U. 2026 item 1003) has been in force since 11 August 2026; its rules on inspections, complaints and fines by the new authority KRiBSI apply from 28 October 2026.
First step: an AI system register and an ISO/IEC 42001 gap analysis in 6 weeks
AI system register with role and risk class
Systems you built, bought or use inside SaaS tools, each with your role, an owner and the reasoning for its risk class.
Review of Article 50 and prohibited practices
Where you must inform, mark or disclose AI content, and which use cases need a decision from the board.
Scope of the AI management system and gap analysis
What already works compared with ISO/IEC 42001, with priorities and a 90-day plan.
You end up with an AI system register with owners and a plan to reach readiness
We agree the fixed scope and date in writing before we start. Request the first step
// Scope
What we do and what we don't
We do
- An AI system register with your role and risk class
- A review of Article 50 duties and prohibited practices
- Annex III classification and deployer procedures
- An AI management system under ISO/IEC 42001, ready for certification
- An AI literacy plan with records of who completed what
We don't
- ISO/IEC 42001 certification: an accredited certification body issues it
- An "AI Act compliance certificate", because no such document exists
- A promise that an ISO/IEC 42001 certificate means AI Act compliance
- Legal opinions in place of your law firm
ISO/IEC 42001 is not a harmonized standard under the AI Act and gives no presumption of conformity. What it does give you is roles, risks and evidence in one place, which is what a supervisor will ask about. Everyday rules for using AI are covered by AI governance and AI security.
// Read more
Related topics and services
More on AI in the enterprise on our blog:
// FAQ
Questions about the AI Act and ISO/IEC 42001
Are we a provider or a deployer?
A provider develops an AI system, or has it developed, and places it on the market or puts it into service under its own name or trademark. A deployer uses an AI system under its authority. A company that rolls out a purchased AI assistant is usually a deployer. A company that sells a product with an AI model under its own brand is a provider. We decide the role system by system.
Does an ISO/IEC 42001 certificate mean AI Act compliance?
No. ISO/IEC 42001 is not a harmonized standard under the AI Act and gives no presumption of conformity. A certificate shows that an AI management system is in place: roles, risk assessment, oversight and improvement. It is a good frame for meeting AI Act obligations and a source of evidence, but the obligations still have to be checked one by one.
We have a subsidiary in Poland. Does anything change there?
Yes. Poland's act on AI systems (Dz.U. 2026 item 1003) has been in force since 11 August 2026. From 28 October 2026, its provisions on inspections, proceedings before the new authority KRiBSI, including complaints, and fines apply (as of 24 September 2026). By then it pays to have an AI system register and a dated Article 50 review.
Do we have to train every employee on AI?
Article 4, as amended by Regulation (EU) 2026/1744, requires measures that support the development of AI literacy among people who operate AI systems on your behalf. It does not require you to guarantee a specific level for each person. In practice, we recommend a plan matched to roles and a record of who completed what.
When is an AI system high-risk?
When it falls into one of the areas in Annex III, such as recruitment or credit scoring, or when it is part of a product covered by the sectoral legislation in Annex I. Obligations for Annex III systems apply from 2 December 2027, for Annex I from 2 August 2028. We write the classification down with its reasoning, because a supervisor will ask for it.
How long does the first step take?
6 weeks, with a fixed scope and date agreed in writing before we start. We quote the price after the first call, once we know how many AI systems the register covers and whether you already run an ISMS under ISO/IEC 27001.
Let's start with your AI system register
In 30 minutes we will establish your role for the AI you use and which obligations apply to you today.
Book a 30-minute callPrefer to start in writing?
Tell us which AI systems you use and we will send back the scope and date of the first step. We reply within one business day.
Request the first step